All byte sizes match but the audit fails.
Compare the actual SHA-256 of the named file with its expected row; restore the correct bytes instead of removing the hash check.
Hands-on recipe
Establish whether a received package has exactly the expected local regular files and byte contents. A checksum manifest detects change relative to a trusted copy; it is not an authenticity signature or media-quality check.
Includes executed local fixtures, scripts and receipts. These checks do not represent a video-generation service run.
node run-recipe.mjs --out ./my-run
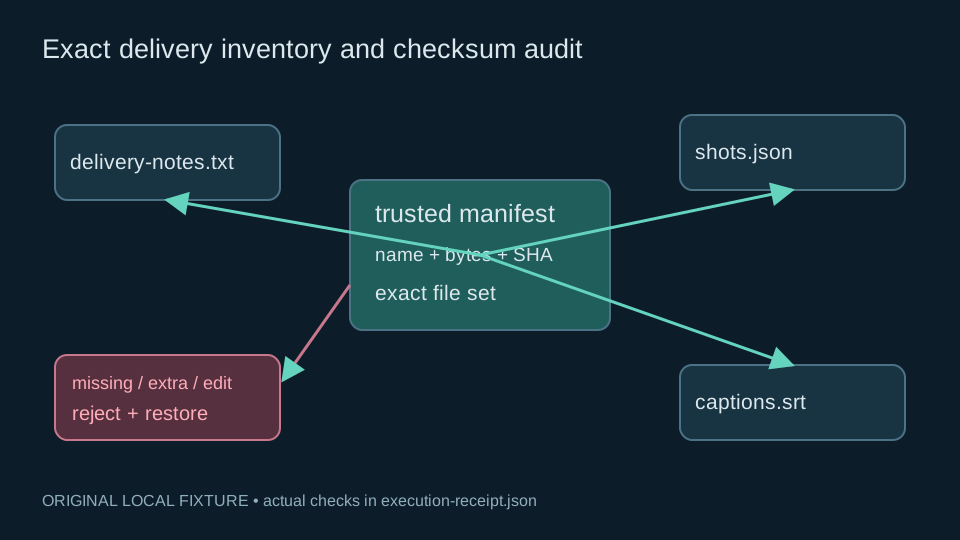
The script writes an original miniature handoff and captures its sorted filename list, byte sizes and SHA-256 values. The expected set is exact: an additional file is reviewable evidence of a mismatch rather than something silently skipped.
Validate unique safe basenames, compare expected and actual inventories, then use lstat to reject a symlink before reading contents. This fixture audits one flat directory, not an arbitrary nested archive or a concurrent untrusted filesystem.
For each expected file, compare both size and SHA-256. The same-size mutation flips one byte of delivery-notes.txt, proving that size alone is insufficient. SHA-256 proves equality to this expected manifest, not that its author is trusted.
The suite temporarily removes a file, adds an extra file, changes bytes and replaces a file with a symlink, always restoring originals in finally. It also rejects duplicate manifest paths and ../outside.txt. The restored package passes again, with nine checks retained.
Compare the actual SHA-256 of the named file with its expected row; restore the correct bytes instead of removing the hash check.
Decide whether that file belongs in the handoff. Remove only the accidental file, or deliberately revise the expected manifest and have it reviewed.
Replace only that entry with a real local regular file, then capture the intended file’s bytes and rerun inventory plus SHA-256 checks.
Keep a trusted manifest and the actual audit receipt with the handoff. The audit does not decode video, establish authorship or protect a manifest that was itself replaced by an attacker.